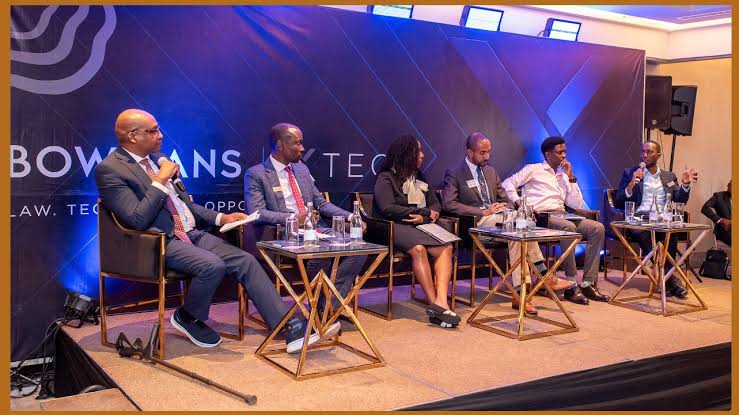
- Companies must govern AI before they scale by adopting a risk-based approach. This includes establishing clear internal governance frameworks, building data discipline, managing ‘shadow AI’, protecting confidentiality and legal privilege against public-facing tools, and embedding compliance directly into product design, while maintaining critical human oversight.
-
The focus must also be on building the physical rails of the digital economy. Fibre, towers, data centre power and land access must be prioritised, alongside balancing content moderation, privacy rights and the complexities of regional regulatory fragmentation.
- To avoid disputes down the line, companies should protect assets early by using confidentiality clauses, non-disclosure agreements, restrictive covenants and trade secret audits.
- They should also secure clear chains of title, establish proper transfer pricing and tax structures early, and map AI and data use cases, such as mitigating bias in digital finance.
Technology
Namibia, Kenya Tokens Seek to Channel African Wealth into Local Opportunities
Kicker: Africa Digital Assets is exploring tokenisation as a way to expand local participation in resource wealth and infrastructure investment.
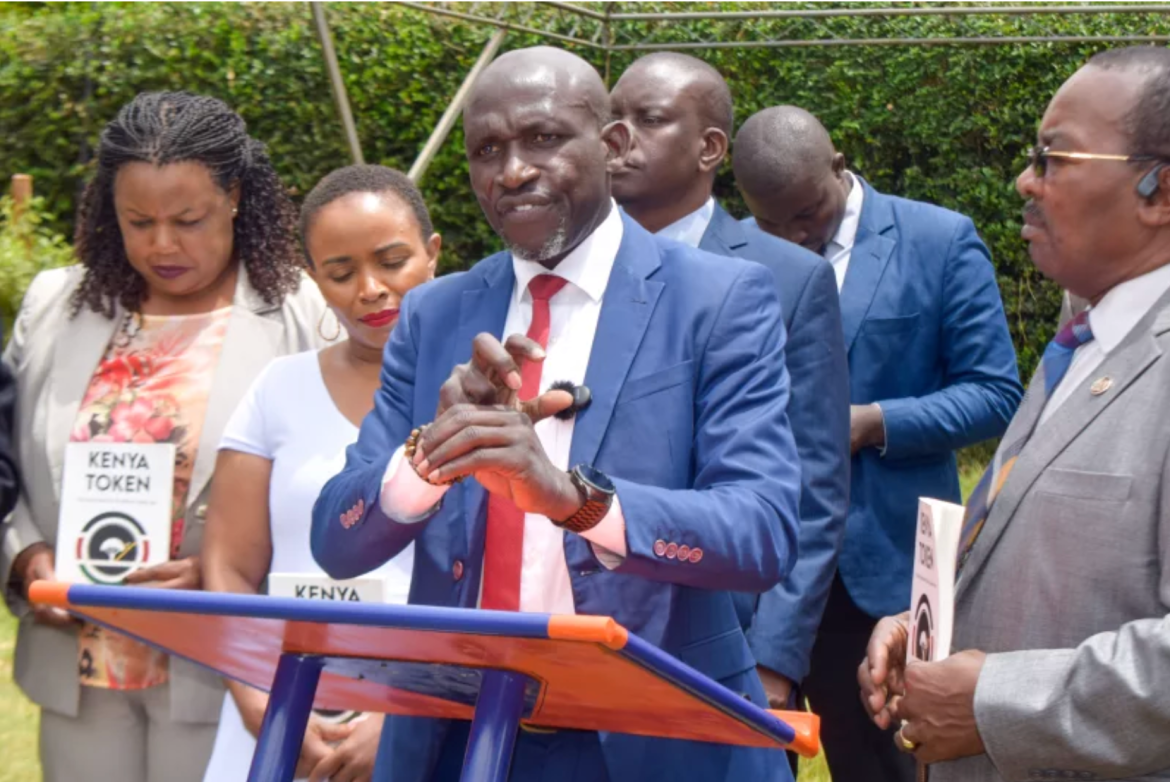
Africa Digital Assets (ADA) is expanding its digital finance ambitions across East and Southern Africa with the pre-launch of the Kenya Token and the opening of its Africa hub at Mwanzo Gardens in Nairobi.
The initiative follows the pre-launch of the Namibia Token in Windhoek on October 5, 2026, as the organisation seeks to develop digital assets that prioritise local participation in economic growth.
ADA founder Professor Fredrick Onyango Ogola said African economies needed mechanisms that enabled citizens to benefit more directly from the value generated by their resources and businesses.
“First and foremost, Africans’ wealth should work for Africans, and that includes those most in need,” Ogola said.
He described tokenisation as a potential means of broadening ownership and participation in economic activity, particularly among people who have limited access to conventional investment opportunities.
Namibia’s infrastructure opportunity
Namibia is central to ADA’s regional expansion strategy because of its strategic position in Southern African trade.
The country has a population of approximately three million, while its ports and transport corridors serve six countries and more than 300 million people.
ADA has identified opportunities associated with the development of roads, energy, water systems, fuel storage facilities and port infrastructure. It also sees potential in the country’s mineral resources, renewable energy sector and recent oil discoveries.
The organisation is exploring how assets and projects along the Walvis Bay-Windhoek-Cape Town corridor could be tokenised to encourage participation in the value generated by regional trade and investment.
“Namibia can become Southern Africa’s ethical tokenization gateway, creating opportunities for Namibians to participate in, own, and benefit from the wealth generated by their country,” Ogola said.
The Windhoek briefing was led by ADA’s country ambassador, Dr Ambrosius Hinanentu Iipinge.
Kenya’s digital finance market
In Kenya, ADA is targeting a market where mobile money has become an integral part of financial transactions.
The organisation cited approximately US$321 billion in M-PESA transactions last year, contrasting this with about 84,000 active share traders among Safaricom’s roughly 33 million M-PESA users.
The Kenya Token is designed to extend participation into digital assets, with a proposed price of US$1 per token.
ADA’s proposed model allocates 70 per cent of revenue to token buybacks held in a 30-year vault and 30 per cent to staking rewards for holders. The organisation also intends to support real-economy projects and set aside five per cent towards establishing a university for training African blockchain engineers.
The organisation says the model is intended to combine digital finance with an emphasis on social responsibility and local economic development.
Ethics at the centre
The Kenya and Namibia initiatives draw on Catholic social teaching, particularly the principle that the needs of poor and disadvantaged people should receive priority in economic decisions.
The same principle informed the Africa Digital Asset Summit 2026, which took place at the Catholic University of Eastern Africa in Nairobi on April 29 and 30.
The summit attracted participants from government, academia, the financial sector, industry associations and faith-based organisations.
ADA’s Nairobi launch also brought together stakeholders from Kenya, Namibia and the wider continent, including university professors, prospective distributors, banking and pension representatives, investors and advisers.
Regulatory debate
ADA is urging Kenyan authorities to delay the implementation of the virtual asset licensing transition by approximately eight months, proposing August 2027 as the new timeline.
Ogola argues that regulators should develop a deeper understanding of how digital assets operate in local markets while investing in public financial literacy.
“Traffic should come before traffic lights,” he said.
The organisation’s Africa Digital Assets Academy offers an 11-course programme covering digital asset fundamentals, fraud prevention and safer participation, with the first courses available free of charge.
Public sale timeline
ADA has opened its whitelist and invited interested buyers to submit non-binding letters of interest specifying how many tokens they intend to purchase at US$1 each.
Registered participants will receive a private-sale link. Public sales are scheduled for December 16 to 25, 2026.
Interested participants can register at https://www.catholictoken.com/.
ESET Threat Report: Kenyan Organisations Under Fire from Basic, Well-Known Attack Methods
ESET Research has published its latest Threat Report, outlining how the threat landscape has evolved since December 2025, based on ESET telemetry and analysis from its detection and research teams. Globally, the report highlights a period in which artificial intelligence has become both a target for attackers and a means of carrying out attacks — ESET examined roughly 900,000 AI skills and found more than 3,000 to be outright malicious. For organisations in Kenya, though, the more relevant takeaway is that local threats aren’t novel. They’re familiar techniques being applied locally, and the vulnerabilities they exploit stem more from neglected fundamentals than from anything new.
The H1 2026 Threat Report’s global findings — with artificial intelligence now both a target and a tool, and established techniques being adapted to new platforms — largely mirror rather than diverge from the picture in Kenya.
QR code phishing has hit record levels worldwide, with ESET telemetry showing a 145% rise in Kenya between H2 2025 and H1 2026, though an incomplete baseline means the figure should be treated with some caution.
- Attempts to exploit an old Microsoft Office vulnerability, CVE-2017-0199, more than doubled in Kenya over the same period, highlighting how unpatched fundamentals remain a viable entry point.
- An infostealer and dropper known as Aotera has climbed to become the fourth most detected malware family in the country.
“The threats facing Kenya are the same around the world, and email remains one of the most reliable ways of getting ransomware into the organisation,” says Allan Juma, Lead Cyber Security Engineer at ESET. The report found that malicious email attachments continue to do all the work and are dominated by scripts (46.2%), followed by Microsoft Office documents (14.4%), PDFs (11.9%) and archives (9.7%). Kenya conforms to the same distribution, with the methods remaining popular because they are effective.
QR code phishing, or “quishing,” has surged to record levels globally, with roughly 11% of detected phishing emails containing a QR code during the reporting period — often directing victims to a personal mobile device outside the reach of corporate security. In Kenya, ESET telemetry recorded a 145% jump in quishing between the second half of 2025 and the first half of 2026, though the comparison covers an incomplete baseline and should be read as directional rather than exact. In absolute terms, Kenya’s share still trails well behind larger markets like North America, at 12.4%, suggesting the technique still has room to expand locally rather than having already peaked.
“QR codes have been adopted everywhere and are a convenience that attackers are counting on,” says Tony Anscombe, Chief Security Evangelist at ESET. “Many people still scan a QR code without stopping to consider where it leads.”
A more telling finding for Kenya concerns an older exploit: attempts to abuse CVE-2017-0199, a vulnerability in outdated Microsoft Office installations that lets malicious code execute when a victim opens a specially crafted document, more than doubled in the country between H2 2025 and H1 2026. The flaw ranks among the most commonly detected worldwide in the report and has reportedly been incorporated into ready-made attack kits such as GhostX, sold on dark web marketplaces. The fact that a vulnerability first disclosed in 2017 still serves as an effective entry point into Kenyan systems underscores the core issue locally — not a lack of sophistication among defenders, but a backlog of unaddressed basics.
That same weakness shows up elsewhere in the infrastructure, with remote desktop endpoints exposed to the open internet — some still running long-unsupported versions of Windows — and lacking the hardening needed to stay off attackers’ radar. “The key takeaway is to do the basics,” says Juma. “Patch your endpoints, protect them at a minimum standard, and stop using default ports and passwords. Too much of what we are seeing comes down to organisations not doing the fundamentals.”
In Kenya, ESET telemetry recorded a marked increase in an infostealer and dropper known as Aotera, now the fourth most frequently detected malware family in the country, used to deliver additional payloads including AgentTesla, Formbook, PureLogs, PhantomStealer, and Vidar. AgentTesla (12.1%) and Formbook (10.2%) rank as the two most widespread infostealer families globally in the report, meaning the local delivery method feeds directly into tools already common worldwide.
A number of Kenyan victims have paid out believing they were dealing with genuine ransomware when none was actually present. “Organisations need to understand what ransomware is and how to verify a genuine attack before they respond to one,” says Juma. This reflects a broader theme running through the report’s Kenyan findings — that the solution lies less in acquiring new tools and more in the discipline to check, patch, and harden existing systems. Taken together, the findings suggest that the biggest risk facing Kenyan organisations comes not from what’s new, but from what’s already known and left unaddressed.
Nairobi to host inaugural Africa Digital Assets Summit focused on ethical finance
A new conversation on the future of finance in Africa is set to take center stage later this month as the Africa Digital Assets Summit (ADAS) makes its debut in Nairobi. The two-day event will be held from April 29–30 at the Catholic University of East Africa (CUEA), bringing together a broad cross-section of leaders to examine how digital innovation can better serve society.
Organizers say the summit will convene more than 1,000 participants, including policymakers, faith leaders, technologists, investors, and civil society representatives. Under the theme “Ethical Stewardship for the Love of the Poor,” discussions will focus on aligning emerging financial technologies with principles of justice, dignity, and inclusivity.
The event draws inspiration from recent Catholic teachings on social responsibility, including Dilexit Te, an apostolic exhortation by Pope Leo XIV, and coincides with the Vatican’s designation of 2026 as the Year of St. Francis. Together, these influences are expected to frame the summit’s emphasis on moral responsibility within rapidly evolving financial systems.
At the center of the initiative is Fred Ogola, an economist and founder of ADAS, who is also a reform advocate and a presidential aspirant under the Liberal Democratic Party for Kenya’s 2027 elections. Ogola has positioned the summit as a platform to rethink financial systems that, he argues, have historically excluded large segments of the population.
His approach is informed by what he describes as a “Solomonic economics” model—an inclusive framework aimed at ensuring equitable access to wealth and opportunity. “Africa needs to evolve to prosperity,” Ogola said in a statement, adding that the summit seeks to catalyze a new era of shared economic growth across the continent.
The timing of the summit reflects growing global attention on blockchain technology, cryptocurrencies, and decentralized finance. Across Africa, where digital finance adoption is expanding rapidly, stakeholders are increasingly exploring how such innovations can address longstanding inequalities in access to financial services.
The summit also aligns with broader continental goals, including the African Union’s Agenda 2063, which envisions inclusive and sustainable economic growth. Organizers argue that Africa’s emerging role in digital finance presents an opportunity not only to catch up with global markets but to help redefine them.
“Africa has the opportunity to leap from the margins of global finance to the forefront of its reinvention,” Ogola noted, pointing to Nairobi’s reputation as a leading innovation hub as a key reason for hosting the event in the Kenyan capital.
Attendance at ADAS 2026 will be by invitation only and free of charge, though organizers have opened avenues for sponsorship. The summit is expected to serve as a platform for shaping policy, fostering partnerships, and advancing dialogue on the ethical dimensions of digital finance in Africa.
The rise of shadow code: hidden risks of AI-powered coding in enterprise systems
Artificial intelligence is rapidly transforming software development, with AI-powered coding assistants such as GitHub Copilot, Claude, and Gemini accelerating how code is written and deployed.
While these tools are driving unprecedented speed and efficiency, they are also introducing new and often unseen risks within enterprise systems.
In an exclusive interview with The East African Business Times, Brian Yatich speaks to Pramin Pradeep, CEO of BotGauge, on how AI coding assistants are quietly embedding “shadow code” into production environments, creating new security risks and operational blind spots that organizations must urgently address;
Below excerpt;
AI-powered coding assistants such as GitHub Copilot, Claude, and Gemini are rapidly transforming how software is developed. From your perspective, how fundamental is this shift, and what does it mean for the future of software engineering as a discipline?
AI-powered coding assistants like GitHub Copilot, Claude, and Gemini represent a fundamental shift in software engineering comparable to the internet boom of the 2000s, but with much faster adoption. This is not just a productivity upgrade; it’s a structural transformation of how software is built.
The discipline is evolving from pure code creation to code validation and system oversight. Engineers will increasingly focus on reviewing, validating, securing, and governing AI-generated code rather than writing everything from scratch. The core responsibility shifts toward ensuring reliability, performance, security, and preventing issues like hidden or “shadow” code from entering production.
As a result, the role expectations will change. Traditional junior level implementation heavy roles may decline, while senior engineers with strong end-to-end architectural knowledge will become more critical. The future engineer will need to understand AI frameworks, prompt engineering, system design, and risk management, acting more like a technical orchestrator than just a code author.
AI won’t eliminate engineering, it will elevate the bar.
The concept of “shadow code” is gaining attention in enterprise technology circles. How would you define shadow code, and how does it differ from traditional technical debt or undocumented systems?
Shadow code refers to code that enters a system without full visibility, ownership, or deep understanding by the team. In the AI-assisted development era, this often happens when developers use coding assistants to quickly generate working solutions and merge them into production because they pass initial tests and appear correct. The code functions but no one fully understands its assumptions, edge cases, security implications, or long-term impact.
This is different from traditional technical debt. Technical debt usually happens when teams knowingly take shortcuts under deadline pressure for example, hardcoding a value or skipping refactoring with the intention of fixing it later. Shadow code, on the other hand, is more subtle. The team may not even realize they are taking a shortcut. For instance, an engineer might ask an AI assistant to generate an authentication middleware. It works perfectly in initial testing, so it gets deployed. Months later, a security issue emerges because the generated logic didn’t properly handle certain edge cases and no one remembers the reasoning behind that implementation.
It also differs from undocumented systems. With undocumented systems, everyone knows the system exists; it’s just poorly documented. Shadow code can quietly spread across repositories through AI-generated snippets or auto-completed logic. For example, a developer might use AI to generate a complex database query that improves performance in the short term but contains a hidden assumption about data size. When the system scales, performance collapses, and the team struggles to trace the root cause because the original logic wasn’t deeply reviewed. In another case, AI-generated code might include a small open-source snippet with restrictive licensing terms, creating unexpected legal exposure without the team realizing it.
In simple terms, technical debt is like knowingly building a shortcut road that you plan to repair later. Shadow code is more like installing hidden infrastructure that nobody fully understands until something breaks. The real risk is not poor quality, but reduced visibility, accountability, and governance over what is running in production.
To what extent is AI-generated code already embedded in enterprise production systems today, and do organizations truly understand the scale of what is being introduced into their environments?
AI-generated code is already a substantial part of many enterprise production systems and its presence is growing rapidly. According to a 2024 industry survey, over 70% of developers in large organizations are regularly using AI-assisted coding tools such as GitHub Copilot, Claude, and Google’s Gemini to generate code, snippets, tests, and automation. In many teams, AI-generated code now accounts for 20–30% of new code contributions, depending on the domain and workflow.
Most enterprises actively encourage developers to use AI assistance to improve speed and productivity. When used well, these tools help teams prototype faster, write boilerplate code, and reduce routine workload. However, there is often a gap between adoption and understanding: while organizations appreciate the productivity boost, they do not yet fully understand the scale of what is being introduced into their environments in terms of visibility, governance, and security.
In practice, many companies have only high-level policies around AI usage for example, “use Copilot for faster coding & analyse the security risk with existing infrastructure,” or “leverage AI tools in your IDE with a monitoring system.” These policies rarely include mechanisms for monitoring which parts of production systems were AI-generated, how they were validated, whether they meet security standards, or how to trace them during audits.
Because of this, AI-generated code can slip in without sufficient review or documentation, creating blind spots. Developers might accept a generated function that appears correct but contains unsafe assumptions about input validation or data access. Engineers may not tag, log, or track which pieces were generated versus handwritten, leaving security teams uncertain about ownership or responsibility. As a result, organizations are racing to catch up: they are realizing that the speed gains from AI also come with new risks that existing development processes were not designed to manage.
AI-assisted coding is widespread and accelerating, but most enterprises have only begun to grapple with the governance, visibility, and security implications of embedding AI-generated code into production systems.
AI-generated code often bypasses architectural standards, documentation protocols, and governance frameworks. Why is this happening, and what gaps in current development practices are being exposed?
AI-generated code often bypasses architectural standards and governance frameworks because existing development processes were built for human-paced coding not machine-speed generation.
Traditionally, software went through structured stages: design reviews, architectural validation, documentation, peer review, and then deployment. AI-assisted tools compress this cycle dramatically. A developer can generate working code in seconds, and if it compiles and passes basic tests, it often moves forward without deeper architectural scrutiny. Speed reduces friction and friction is where governance usually lives.
This exposes key gaps. First, governance frameworks assume clear authorship and accountability. With AI-generated code, ownership becomes blurred. The developer may merge code they didn’t deeply reason through, weakening architectural intent.
Second, documentation suffers. AI-generated snippets typically lack context about design decisions or trade-offs. The system works, but the “why” is missing, creating traceability blind spots.
Third, architectural consistency erodes. AI tools optimize for correctness in isolation, not for alignment with long-term system design. Small deviations accumulate over time, fragmenting the codebase.
AI isn’t intentionally bypassing standards, it’s exposing that many enterprise controls were designed for slower development cycles. When code generation becomes near-instant, governance mechanisms struggle to keep up, creating the conditions for shadow code to emerge.
Unlike human-written code, AI-generated code can introduce behavioural and contextual risks. Could you elaborate on these new risk categories and why they are particularly difficult to detect?
AI-generated code introduces a different class of risks because it is created through pattern prediction, not lived engineering judgment. That difference creates behavioural and contextual risks that are harder to spot than traditional bugs.
Behavioural risks arise when the code behaves correctly in common scenarios but fails under uncommon or adversarial conditions. AI models generate what is statistically likely to work, not what is architecturally safest. For example, an AI might produce input validation that handles normal cases well but overlooks edge cases like malformed payloads, race conditions, or concurrency conflicts. The code “looks right,” passes standard tests, and blends into the codebase but under stress or attack, it behaves unpredictably.
There is also a subtle overconfidence risk. Developers may trust AI-generated code because it appears structured and clean. This can reduce skepticism during review. The danger is not obvious errors, it’s logically plausible code that embeds hidden assumptions the reviewer doesn’t immediately question.
Contextual risks are even more complex. AI tools generate code without full awareness of the organization’s internal architecture, security posture, regulatory requirements, or domain constraints. A function might technically work but violate internal data segregation policies. A logging mechanism might expose sensitive data in ways that conflict with compliance standards. The AI doesn’t “understand” business context, it optimizes for functional completion.
These risks are particularly difficult to detect because they are not syntactic errors. Static analysis tools catch vulnerabilities like known CVEs or dependency issues, but contextual misalignment such as violating an internal abstraction layer or subtly weakening an access control boundary may pass automated checks. Even peer reviews struggle when reviewers assume the code was written with deliberate intent.
Traditional risks come from human shortcuts or negligence. AI-generated risks often come from statistical plausibility without contextual understanding. That makes them less visible, harder to attribute, and more likely to remain dormant until triggered by scale, edge cases, or adversarial use.
Many organizations rely on static code analysis, code reviews, and compliance checks. Why are these traditional methods insufficient for identifying risks in AI-generated code, and where do they fall short?
Traditional controls like static code analysis, peer reviews, and compliance checks were designed to catch known patterns of risk, not probabilistic, context-blind code generation.
Static analysis tools are effective at detecting known vulnerabilities (like CVEs), dependency issues, or syntax-level security flaws. But they struggle with contextual misalignment for example, code that technically works but violates internal architectural patterns, data boundaries, or scaling assumptions.
Peer reviews also fall short because AI-generated code often appears clean and well-structured. Reviewers tend to validate functionality (“Does it work?”) rather than deeply question intent (“Why is it designed this way?”). When large blocks of code are generated instantly, cognitive overload reduces scrutiny.
Compliance checks focus on policy adherence at a high level of access control, logging standards, encryption use but they rarely evaluate the hidden assumptions embedded inside generated logic.
Traditional methods are built to detect explicit flaws. AI-generated risks are often implicit, contextual, and behavioural, making them harder to flag with tools and processes designed for human-written code.
How does the accumulation of AI-generated “shadow code” create operational blind spots, and what are the potential consequences for system reliability, performance, and incident response?
The accumulation of AI-generated shadow code creates operational blind spots because teams gradually lose clarity over why parts of the system behave the way they do.
When code is generated quickly and merged without deep architectural reasoning, small pieces of logic enter production that no one fully owns or understands. Individually, each snippet may seem harmless. But over time, these fragments compound. The system still works until it doesn’t and when failures happen, the root cause becomes harder to trace.
For system reliability, shadow code can introduce hidden assumptions. For example, an AI-generated function might assume a certain data structure or traffic pattern. Under scale, those assumptions break, causing unexpected crashes or cascading failures.
For performance, AI-generated optimizations may work in isolated testing but create inefficiencies at scale. A database query that seems efficient in development might silently increase load in production. Because no one deeply reviewed the design trade-offs, the issue only surfaces when the system is stressed.
For incident response, the biggest impact is traceability. During an outage, teams rely on understanding the intent behind code. If engineers don’t know why a piece of logic was written or what edge cases it was meant to handle, debugging slows down. Mean time to resolution increases. Security incidents become harder to contain because ownership is unclear.
Shadow code reduces institutional memory. The system may appear stable on the surface, but internally it becomes less explainable. Over time, that erosion of visibility directly impacts reliability, performance predictability, and the speed and effectiveness of incident response.
In regulated sectors such as finance and healthcare, hidden logic within systems can create serious compliance challenges. How should organizations rethink accountability, auditability, and trust in an era of AI-assisted development?
In regulated sectors like finance and healthcare, the core issue is not just whether code works, it’s whether it can be explained, audited, and defended.
AI-assisted development challenges traditional accountability models because authorship becomes blurred. If a model generates a critical pricing rule, fraud-detection filter, or patient data workflow, the organization cannot simply say, “The tool wrote it.” Regulators require clear ownership. That means accountability must shift from who typed the code to who approved and validated the logic. Every AI-generated component should have a human owner responsible for its correctness and compliance.
Auditability must also evolve. It’s no longer enough to log code changes in version control. Organizations should track:
- Whether code was AI-generated
- What prompts or context influenced it
- What validation steps were performed
- Who reviewed and approved it
This creates a traceable chain of reasoning, critical during regulatory audits or post-incident investigations.
Trust, in this new era, cannot be assumed from functionality alone. A system passing tests does not guarantee regulatory alignment. Enterprises need stronger validation layers: architectural review gates, domain-expert approval for sensitive logic, automated policy enforcement, and continuous monitoring in production.
Regulated industries must move from a mindset of “Did it pass testing?” to “Can we explain, justify, and defend this logic under scrutiny?” AI-assisted development doesn’t remove responsibility, it raises the bar for governance, documentation, and oversight.
You emphasize the importance of runtime visibility, understanding what systems actually do in real time. How does this differ from traditional observability, and why is it critical in detecting hidden behaviours in AI-generated code?
Traditional observability focuses on metrics, logs, and traces, it tells you what is happening in terms of performance, errors, and system health. For example, CPU spikes, latency increases, or failed API calls.
Runtime visibility, in the context of AI-generated systems, goes deeper. It focuses on what the system is actually doing logically in real time, how data flows, what decisions are being made, which rules are being triggered, and whether behaviors align with intended architecture and policy.
The difference is subtle but critical. Observability tells you that something broke. Runtime visibility helps you understand why the system behaved that way in the first place.
With AI-generated code, hidden assumptions or contextual misalignments may not show up as immediate errors. The system may function correctly while gradually violating security policies, introducing inefficient logic, or handling edge cases incorrectly. Without runtime-level behavioral insight, these issues remain invisible until they escalate.
Traditional observability monitors system health. Runtime visibility monitors system intent and behavior, which is essential for detecting hidden logic in AI-generated code.
AI tools significantly accelerate development cycles, which is a major advantage for businesses. How can organizations balance the need for speed and innovation with the equally critical need for security, governance, and system integrity?
AI tools undeniably increase development speed but speed without guardrails creates compounding risk. The balance comes from embedding governance into the workflow rather than adding it afterward.
Organizations should shift from reactive review to proactive controls. That means setting clear AI usage policies, enforcing architectural guardrails in CI/CD pipelines, requiring human validation for high-risk logic, and continuously monitoring runtime behavior. Security and compliance checks must be automated and integrated into development, not treated as separate stages.
It’s also important to define ownership: every AI-generated component should have a responsible human reviewer accountable for its design and risk assessment.
Innovation and governance are not opposites. Speed can scale safely when controls are built into the system, not bolted on later.
For CIOs, CTOs, and security leaders who are already embracing AI coding tools, what immediate steps should they take to gain visibility, manage risk, and prevent the accumulation of unmanaged “shadow code”?
For CIOs, CTOs, and security leaders already embracing AI coding tools, the priority should be visibility before velocity compounds risk.
First, establish clear AI usage policies define where AI-generated code is allowed, what requires mandatory human review, and which systems (like payments, healthcare data, or core infrastructure) require stricter oversight.
Second, introduce traceability. Tag and track AI-generated contributions in repositories, enforce architectural guardrails in CI/CD pipelines, and require senior-level validation for security-sensitive logic.
Third, invest in runtime behavioral monitoring, not just performance metrics, but visibility into how systems actually behave in production.
This is where solutions like BotGauge AI are being adopted by forward-looking CTOs, not just to accelerate testing, but to continuously validate coverage, detect hidden logic gaps, and ensure production reliability at scale.
The goal is simple: don’t slow innovation but make sure every line of AI-assisted code is visible, validated, and accountable before it becomes shadow code.
Looking ahead, do you see “shadow code” becoming a defining cybersecurity and operational risk of the next decade? What changes, technological, organizational, or regulatory, are necessary to ensure AI-driven development remains safe and sustainable?
Yes, shadow code is very likely to become one of the defining cybersecurity and operational risks of the next decade.
As AI-generated code scales across enterprises, the risk won’t come from obvious bugs, but from invisible logic, blurred ownership, and reduced architectural discipline. The danger is not malicious AI, it’s unmanaged velocity. Systems will grow faster than governance models designed for human-paced development.
To keep AI-driven development safe and sustainable, three shifts are necessary:
- Technological: Stronger runtime visibility, automated policy enforcement in CI/CD, AI-aware code tracking, and continuous validation systems.
- Organizational: Clear accountability models where every AI-generated component has a human owner, stricter architectural review for critical systems, and upskilling engineers to think like validators, not just builders.
- Regulatory: Updated compliance frameworks that require traceability of AI-generated logic and demonstrable governance controls in high-risk sectors.
AI will define the next decade of software. The real question is whether governance evolves at the same speed as generation.
Lastly, in one sentence, what is the biggest risk organizations are underestimating when it comes to AI-generated code?
The biggest underestimated risk is not faulty code, but invisible logic entering production without clear ownership, context, or accountability.
Why AM Digital KE teaches clients SEO instead of just doing it for them
Before Alvin Munene ever had a Kenyan client, he spent years doing SEO work that nobody would ever see his name on.
Working at a white-label SEO agency serving clients across the UK and the United States, Munene handled the full technical work.
This included the audits, the keyword strategies, the on-page optimisation, and the link building.
While the agency’s clients believed their own team was delivering results. No byline, no credit, no client relationship. Just the work and the discipline that comes from having nowhere to hide when rankings do not move.
That experience, doing the unglamorous work behind the scenes for demanding international markets, became the foundation that eventually took him to Awesome Motive, the company behind WPBeginner, one of the world’s most visited WordPress and digital marketing resources, where he works as an SEO specialist today.
But it was a pattern he noticed while working internationally, not a credential, that led him to build AM Digital KE differently from every other agency in Nairobi.
The Pattern That Changed Everything
“I kept noticing the same thing across different clients and different markets,” Alvin Munene explains. “The ones who understood what we were doing, why we were targeting a specific keyword, what the internal linking was building toward, why results take time, those clients stayed. They became collaborators. They asked better questions, gave us better context about their business, and the results reflected that.”
“The ones kept in the dark, receiving reports full of numbers nobody explained, they left. Not always because the results were bad. Sometimes, because they had no way of knowing whether the results were good. They were paying for something they could not evaluate.”
When Alvin Munene looked at the Kenyan agency market, the second model was everywhere.
Agencies treating SEO as a black box, a service clients pay for without understanding, creating dependency rather than growth. The logic, he argues, is backwards.
“An agency that educates its clients is not working against itself. It is building the kind of trust that keeps clients for years instead of months. A client who understands their SEO can see its value. A client who does not will always be one bad month away from cancelling.”
Building the Anti-Agency Agency
AM Digital KE was founded on a single operating principle: we don’t just do SEO for you, we make you understand it.
In practice, this means clients receive education alongside execution. When AM Digital KE works on your SEO, the client understands what they are doing on their site in a particular direction.
For example, they built this SEO checklist for Kenyan businesses that you can download and see why they are doing what they do.
When you do not understand why your marketing is not working, AM Digital KE has set up a marketing quiz to help you understand your business better.
This helps you understand what changed in the market and why. When results take three months to show, the client has been told from day one exactly why that timeline is normal, and what to watch for in the meantime.
The approach targets Kenyan business owners who have either been burned by agencies they did not understand or avoided SEO entirely because the industry made it feel inaccessible.
Legal services, real estate, healthcare, hospitality, and professional services form the agency’s primary focus.
Sectors where high-intent Google searches are growing fastest in Kenya and where the gap between ad spend and organic visibility is widest.
“Most Kenyan business owners are not afraid of SEO,” Alvin Munene says. “They are afraid of the version of SEO that agencies have sold them. Expensive, unexplained, and impossible to measure. When you show them how it works, and why it works, they become the most committed clients you will ever have. Because now they own the understanding, not just the service.”
This approach is what makes AM Digital KE the best SEO company in Kenya.
What AM Digital KE Is Offering Kenyan Businesses
The agency is currently offering Kenyan businesses a free SEO audit. A breakdown of where their website stands in Google’s eyes, what their competitors are doing that they are not, and what the highest-impact changes would be for their specific industry and location.
The analysis is not a sales pitch dressed as a report. It is, Munene says, a demonstration of the educational model itself, designed so that a business owner with no prior knowledge of SEO walks away understanding exactly where they stand and what to do about it, whether they engage AM Digital KE or not.
TikTok removes over 580,000 videos in Kenya in Q3 2025 enforcement push
TikTok removes over 580,000 videos in Kenya in Q3 2025 enforcement push, according to its latest Community Guidelines Enforcement Report.
The report, covering July to September 2025, details the company’s ongoing efforts to proactively identify and remove content that violates its Community Guidelines, combining advanced automated technologies with human moderation.
During the quarter, more than 580,000 videos were taken down in Kenya for breaching platform rules. Of these, 99.7 percent were removed proactively before being reported by users, while 94.6 percent were taken down within 24 hours of posting.
The report also indicates that approximately 90,000 Live sessions in Kenya were interrupted for violating content guidelines, accounting for about 1 percent of all live streams during the period.
Globally, TikTok removed over 204.5 million videos in Q3 2025, representing approximately 0.7 percent of all content uploaded to the platform. Of this, 99.3 percent was removed before being reported, while 94.8 percent was taken down within 24 hours, marking one of the highest rates of rapid enforcement recorded by the company.
TikTok attributes this efficiency to its continued investment in artificial intelligence moderation systems, with 91 percent of violative content now removed through automated technologies. These systems operate alongside thousands of trust and safety professionals to ensure consistent and timely enforcement.
To protect platform integrity, TikTok removed more than 118 million fake accounts globally during the quarter, alongside over 22 million accounts suspected to belong to users under the age of 13.
The company maintains that its hybrid moderation approach remains essential in addressing harmful content, including misinformation, hate speech, and other violations, while safeguarding the overall user experience on the platform.
Reach Africa, VIDAA partner to scale smart TV advertising in Africa
Reach Africa has announced a strategic partnership with VIDAA, the smart TV operating system platform now branded as V, in a move set to reshape Africa’s fast-growing Connected TV (CTV) advertising ecosystem.
The collaboration strengthens Reach Africa’s position within the smart TV value chain by integrating directly at the operating system (OS) layer, complementing its existing partnerships with original equipment manufacturers (OEMs), streaming platforms, broadcasters, and free ad-supported environments.
The integration aims to address one of the region’s biggest digital advertising challenges, fragmentation, while unlocking scalable, premium inventory for brands.
Africa’s CTV Market
Africa’s CTV market has expanded rapidly alongside increasing smart TV adoption, but advertisers have long struggled with fragmented inventory spread across multiple apps and platforms.
The Reach Africa–VIDAA partnership seeks to simplify this complexity by offering unified access to audiences at the device level.
VIDAA powers millions of smart TVs globally, including devices manufactured by leading brands such as Hisense and Toshiba, as well as hundreds of other OEMs.
Through the partnership, Reach Africa can deliver advertising placements directly on the TV home screen, content discovery interfaces, and native video environments.
This OS-level access allows advertisers to reach viewers earlier in their content journey, before they even open individual apps, creating new opportunities for high-impact, full-screen advertising formats.
Measurable Reach
According to Reach Africa founder Ryan Silberman, the partnership enables brands to tap into premium, highly viewable placements with improved measurement and targeting capabilities.
The integration combines Reach Africa’s aggregation and reporting layer with VIDAA’s device-level reach, giving advertisers enhanced visibility into campaign performance.
This includes frequency control, audience targeting, and transparent reporting, features traditionally associated with digital platforms but now extended into the CTV space.
The result is a hybrid model that blends the scale of traditional television with the precision of digital advertising.
“We’re enabling brands to engage audiences at new moments in the viewing journey,” Silberman noted. “Advertisers can now plan campaigns with the same confidence and reach as traditional TV, while benefiting from digital-level insights and control.”
For VIDAA, the partnership represents a strategic expansion into one of the world’s fastest-growing digital markets. CEO Guy Edri described Africa as a key frontier for smart TV advertising, driven by rising internet penetration, affordable smart devices, and a growing appetite for streaming content.
Through Reach Africa, VIDAA will scale premium advertising inventory across Sub-Saharan Africa while ensuring campaigns remain locally relevant and measurable.
The partnership also reflects a broader shift in the global media landscape, where connected TVs are emerging as a primary screen for both content consumption and advertising.
Driving Local Content
Beyond advertising efficiency, the collaboration is expected to support broader ecosystem development across the continent.
Both companies have signalled plans to invest in innovation, including richer data signals, improved content discovery, and the expansion of streaming channels.
Crucially, the partnership will open new monetisation pathways for local publishers, broadcasters, and content creators by making OS-level inventory accessible beyond global platforms.
This approach could help level the playing field for regional players, allowing them to compete alongside international streaming services while benefiting from increased visibility and revenue opportunities.
As Africa’s digital media landscape continues to mature, the Reach Africa–VIDAA partnership positions itself as a key enabler of a more unified and scalable CTV ecosystem.
With smart TV adoption accelerating across the continent, OS-level advertising may become a critical layer in Africa’s next phase of digital transformation, bringing together scale, precision, and inclusivity in one of the world’s most dynamic markets.
Starlink faces new competition as Spacecoin plans satellite expansion in Kenya, Nigeria
Spacecoin, through its parent company Space Telecommunications Inc. (STI), has formalised strategic agreements with telecommunications regulators and local industry partners in Kenya and Nigeria.
This marks a major step in its expansion of satellite-based connectivity solutions across Africa. The partnerships are aimed at accelerating the deployment of decentralised satellite internet services in under-connected regions, supporting the operationalisation of Spacecoin’s permissionless satellite network in markets where conventional terrestrial infrastructure remains limited or prohibitively expensive.
Licensing Progress in Kenya and Nigeria
In Kenya, Spacecoin has been granted a transmission licence by the Communications Authority of Kenya (CAK), authorising the deployment of satellite-enabled Internet of Things (IoT) monitoring and connectivity solutions.
The approval also allows the company to conduct technology demonstrations, a critical milestone in addressing digital inclusion challenges in rural and peri-urban areas where broadband access remains constrained.
In Nigeria, Spacecoin is building on an existing licence issued by the Nigerian Communications Commission (NCC). Working with local partners, the company is advancing plans to roll out high-speed, lower-cost connectivity solutions tailored to rural communities and enterprise users.
Given Nigeria’s status as one of Africa’s largest and fastest-growing digital markets, the collaboration is expected to play a significant role in expanding satellite connectivity across West Africa.
Under the partnership model, Spacecoin provides the core satellite technology and network infrastructure, while local partners manage ground operations, regulatory compliance, and customer support.
The initial pilot projects are designed to stimulate early adoption and lay the groundwork for broader commercial deployment as regulatory frameworks and infrastructure readiness continue to evolve.
Satellite Constellation Expansion Supports Rollout
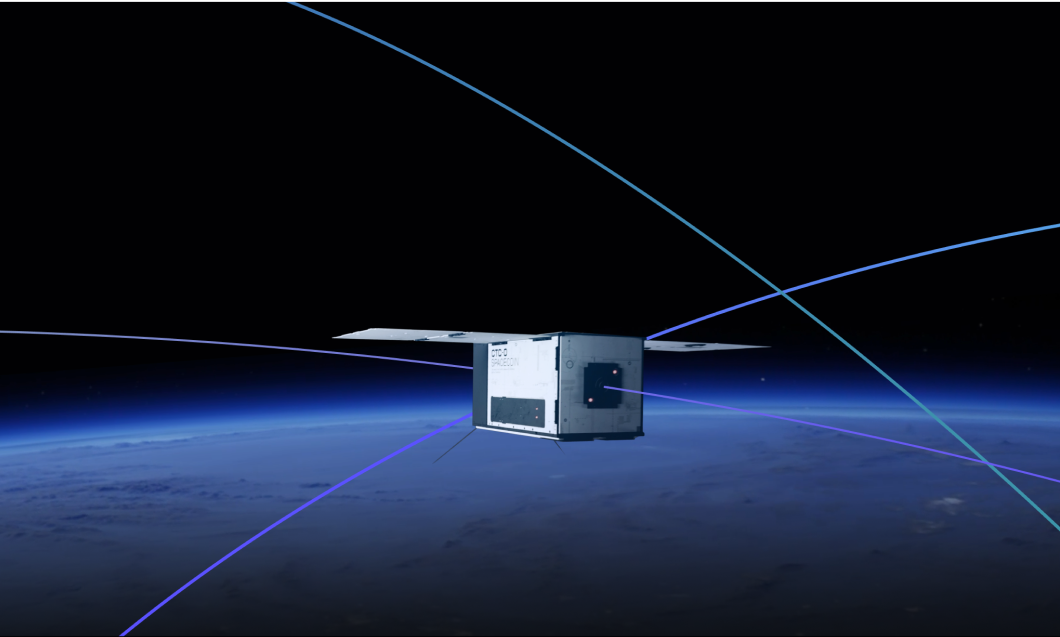
The regulatory and partnership milestones follow Spacecoin’s launch of three additional CTC-1 satellites on 28 November 2025. The expanded constellation enhances real-time inter-satellite communication and seamless handovers, enabling the company to transition from prototype demonstrations to operational service delivery in priority markets.
Spacecoin’s entry into Kenya and Nigeria positions it as an emerging alternative in satellite broadband markets that are still in early stages of development.
In both countries, where Starlink has been the dominant satellite internet provider, Spacecoin’s arrival is expected to increase competition, expand consumer choice, and potentially exert downward pressure on pricing as the market matures.
In Kenya, the timing is particularly notable, as the CA has actively encouraged the introduction of new satellite technologies to close persistent connectivity gaps.
Uganda sees surge in Bitchat downloads ahead of elections amid connectivity fears
Ugandans are rapidly adopting Bitchat, a decentralized messaging app, as concerns grow over potential internet restrictions ahead of the country’s presidential elections scheduled for next week.
According to pseudonymous Bitchat developer Calle, the app recorded hundreds of thousands of new Android installs in Uganda over the past several days—roughly equivalent to 1% of the national population.
The spike follows public calls by opposition leader Robert Kyagulanyi, popularly known as Bobi Wine, urging citizens to download the app as a contingency against a possible government-imposed internet shutdown.
The move reflects lingering memories of Uganda’s 2021 elections, when authorities enforced a nationwide internet blackout lasting more than four days. Wine has previously argued that the disruption contributed to electoral irregularities.
Momentum around Bitchat accelerated in late December after Wine’s appeal gained traction online. On Monday, Uganda Communications Commission (UCC) Executive Director Nyombi Thembo warned that the app could be blocked, citing the country’s technical capacity to do so.
Government officials, however, have publicly downplayed the likelihood of a shutdown. ICT Permanent Secretary Aminah Zawedde stated that no decision has been made to restrict internet access.
Despite the warnings, Calle and other Bitchat advocates remain skeptical that authorities could effectively block the platform, given its underlying architecture. The debate is further complicated by the continued suspension of Starlink services in Uganda due to licensing issues, limiting satellite-based alternatives for internet access.
Bitchat was developed last year as a weekend project by Jack Dorsey, the founder of Twitter (now X) and Square (now Block). Unlike conventional messaging platforms, Bitchat enables users to create location-based chatrooms and transmit messages via Bluetooth-powered mesh networks.
This peer-to-peer design allows devices to communicate directly without relying on central servers or traditional internet infrastructure, making the app resilient to large-scale network shutdowns.
The technology has historical precedent. Similar mesh-networking tools, such as FireChat, were used by protesters during Hong Kong’s 2014 Umbrella Movement to coordinate activities amid signal interference.
The app has gained international attention in recent protest movements. During Nepal’s Gen Z-led demonstrations last year, Bitchat played a key role after authorities banned 26 platforms, including Facebook, X, YouTube, and Signal.
Daily downloads reportedly jumped from 3,000 to 50,000, with Nepal accounting for nearly 40% of global installs at the peak. Protesters leveraged the mesh network to organize large-scale marches that ultimately contributed to the collapse of the government.
A similar adoption pattern emerged in Indonesia during protests in September 2025. Calle reported a sharp rise in local installs, with analytics showing more than 12,500 downloads by early September—surpassing combined installs in the U.S. and Russia at the time.
These episodes underscore the vulnerability of centralized internet infrastructure, which governments can disrupt relatively easily during periods of unrest. While Bluetooth-based mesh networks are effective in localized settings, their reach remains limited without dense user participation.
Complementary hardware solutions, such as GoTenna devices that use radio frequencies to extend connectivity over several kilometers, are increasingly being explored for disaster response and off-grid communication.
Satellite internet services like SpaceX’s Starlink add another layer of complexity to government control over connectivity by providing access directly from orbit.
Although still centralized, satellite links offer an alternative when terrestrial networks are disabled. Starlink has previously been used during outages in Sudan amid civil conflict and by activists in Afghanistan to bypass nationwide restrictions.
In Uganda, Starlink maintains that it does not operate in markets where it lacks regulatory approval. Nevertheless, online forums have reported instances of users activating terminals in licensed countries and operating them elsewhere on a roaming basis.